Ph.D. in Computing Science, Umeå University, Sweden — 2020–2024
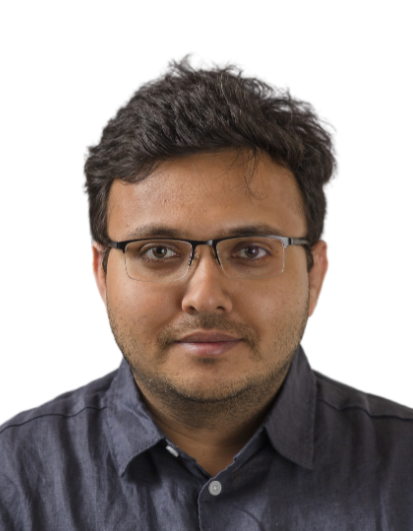
Sourasekhar Banerjee, Ph.D.
Postdoctoral Researcher
Department of Information Technology
Uppsala University, Sweden
Email: sourasekhar.banerjee@it.uu.se
Phone: +46 730 987 453
Research Interests
My research lies at the intersection of federated learning, privacy-preserving machine learning, and distributed AI systems, focusing on four theoretically grounded and practically validated themes:
- Personalization and Heterogeneity — Provably convergent FL algorithms that handle non-IID data and systems heterogeneity across large-scale distributed environments.
- Continual Federated Learning — Frameworks for adapting federated models to distributional shifts without catastrophic forgetting, applied to adaptive intrusion detection in IoT networks.
- Trustworthy Federated Learning — Quantifying and mitigating privacy leakage and adversarial threats in FL pipelines, with applications to verifiably secure distributed learning across IoT and cross-institutional settings, and explainability of the clients.
- Explainable Federated Learning — Privacy-preserving frameworks that attribute global model behavior to individual client contributions, turning FL into an auditable system that supports anomaly detection, fair valuation, and accountability in high-stakes domains.
- Applied Federated Learning — User-centric FL for continuous sensing environments, including cognitive health, image privacy, and cross-institutional collaboration under data scarcity.
Education
M.Tech. in Computer Science & Engineering, University of Calcutta, India — 2016–2018 (First Class, 82.83%)
M.Sc. in Computer Science, University of Calcutta, India — 2014–2016 (First Class, 75.54%)
B.Sc. in Computer Science (Hons.), St. Xavier’s College, India — 2011–2014 (First Class, 71%)
Research Experience
Postdoctoral Researcher — Department of Information Technology, Uppsala University, Sweden
- Developed a domain continual learning-based intrusion detection system for RPL-IoT attack domains, evaluating catastrophic forgetting under distributional shift across heterogeneous IoT traffic.
- Designing a domain continual learning framework for aggregation-free event-driven federated learning using knowledge distillation, to reduce catastrophic forgetting caused by spatio-temporal data heterogeneity in distributed IoT environments. (Ongoing)
- Investigated the use of the MOMENT foundation model for multi-class attack identification in RPL-based IoT networks, demonstrating competitive attack detection and effective differentiation among Blackhole, DIS Flooding, Worst Parent, and Local Repair attacks.
- Developed an LSTM-based intrusion detection system for RPL-based IoT networks that enhances attack detection by integrating TX/RX radio features with routing-layer features, achieving up to ~4% improvement in F1-score across DIS-Flooding, Local Repair, and Worst Parent attacks.
- Developed FedLIME, a clustered federated learning method that groups clients by LIME attribution (explainability) divergence instead of weight similarity. (Ongoing)
Research Intern — Institute of High Performance Computing, A*STAR IHPC, Singapore
- Designed a Federated Image Privacy Advisor using personalized FL daisy-chaining, achieving a 30% improvement in privacy scoring accuracy over global FL baselines. Conducted multi-modal (text + image) FL experiments; compared privacy risks under global and personalized FL settings across multiple attack scenarios.
Doctoral Researcher — Department of Computing Science, Umeå University, Sweden
- Authored and defended a Ph.D. thesis covering personalized FL algorithms, feature selection, straggler mitigation, event-memorability and privacy risk prediction.
- Designed scalable personalized FL algorithms addressing statistical heterogeneity (non-IID distributions) with rigorous convergence analysis.
- Developed privacy risk prediction models quantifying per-client leakage as a function of model architecture and aggregation strategy.
- Built personalized FL models for cognitive science (event memorability prediction).
Research Fellow — Department of Computer Science & Engineering, IIT Patna, India
- Designed an edge-deployable computer vision model for banned object detection in real-time.
- Delivered an embedded ML solution optimised for resource-constrained edge environments, resulting in a granted Indian patent.
Technical Skills
- Federated Learning Frameworks: FEDn, Flower, NVIDIA FLARE
- ML / Data Science: Federated Learning, Continual Learning, Personalised ML, Statistical Optimisation, Feature Selection, Predictive Modelling, Time-Series Modelling, Multi-modal Analysis, Anomaly Detection, Privacy-Preserving AI
- Deep Learning: CNN, LSTM, GAN, VAE, Transformers, Autoencoder, Diffusion Models
- GenAI / LLM: RAG, vector databases, Agentic AI, Fine-tuning, LoRA/PEFT
- Data Science Stack: Python, PyTorch, scikit-learn, pandas, NumPy, Matplotlib, Seaborn, SQL
- MLOps / DevOps: Docker, Kubernetes, Git, GCP, Azure
- Programming Languages: Python, JAX, C/C++, Java